A strong female voice for Islam
The International Conference on Islamic Feminism currently underway in Barcelona calls "gender jihad" to sexist readings of Islamic sacred texts. Here is an excerpt from Abdennur Prado's keynote call to arms:
"Opposing this internal criticism (deconstruction of the patriarchy based on the sources of Islam), we consider that Western culture's claim to superiority is not an effective adversary against fundamentalism, as this attack fails in his objective and tends to inflame even further these opposing stances. The more aggressive the pro-westernisation stance is and the more it relies on arguments based on a fear of Islam, the more strength is gained by the fundamentalist movements that present themselves as defenders of their religion in the face of these attacks 'from outside'.
Nor are attempts at 'social engineering' effective, such as that of Kemal Ataturk, put in practice in Turkey - banning the veil, closing the sufi associations, substituting the Arabic alphabet for the Latin alphabet, repressing all public expression of religious acts, etc. The failure of this policy could not be more spectacular. The social engineering and spread of anti-religious secularism carried out has not achieved its aim. In fact, Turkey has gone from being a region characterised by syncretism, the mixing of cultures and religious pluralism, to be a country in which traditional Islam is threatened by political Islam (Islamism)."
Friday, October 28, 2005


Wednesday, October 26, 2005
Twins for Hitler? A fresh face for fascism?
While surfing some religious blogs this morning, the photo below caught my eye on a blog called doxology. Here is an excerpt from the underlying ABC story:
"They may remind you another famous pair of singers, the Olsen Twins, and the girls say they like that. But unlike the Olsens, who built a media empire on their fun-loving, squeaky-clean image, Lamb and Lynx are cultivating a much darker personna. They are white nationalists and use their talents to preach a message of hate."
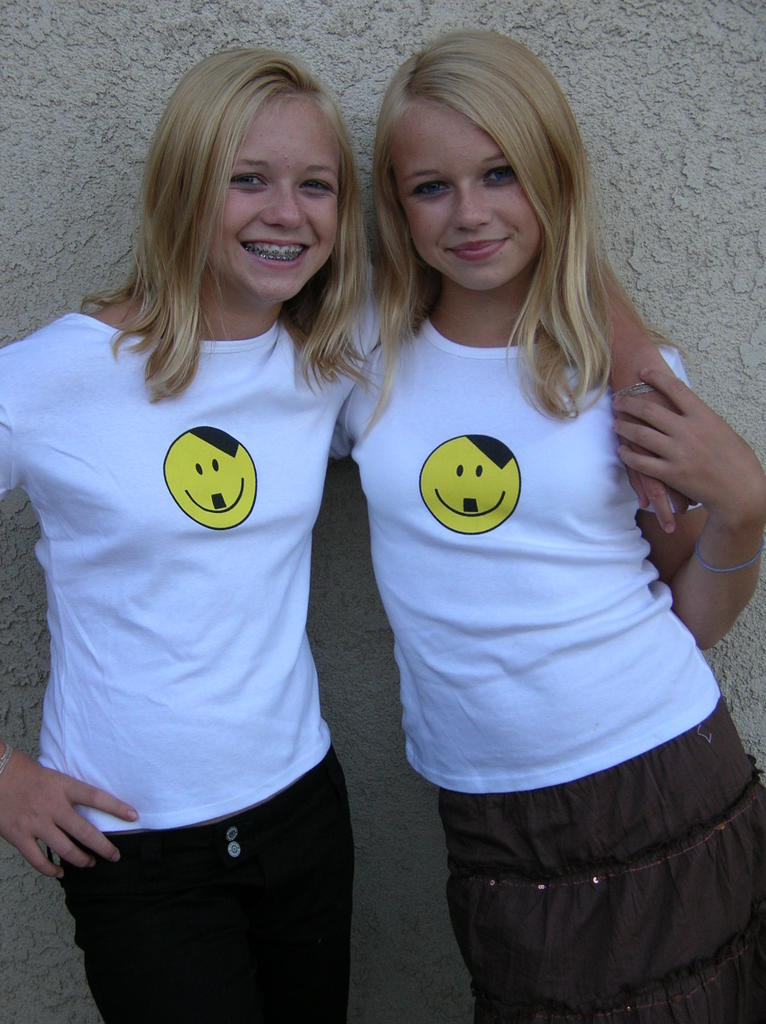
While surfing some religious blogs this morning, the photo below caught my eye on a blog called doxology. Here is an excerpt from the underlying ABC story:
"They may remind you another famous pair of singers, the Olsen Twins, and the girls say they like that. But unlike the Olsens, who built a media empire on their fun-loving, squeaky-clean image, Lamb and Lynx are cultivating a much darker personna. They are white nationalists and use their talents to preach a message of hate."
Tuesday, October 25, 2005
Inside a penetration testing shop
Its one thing to build Nessus on your Linux box, click all tests on, enter a target IP, click go, and watch the test progress bar grow. After hundreds of thousands of Ethernet TX/RX LED flickers, Nessus will present you with a nicely formatted report of any and all vulnerabilities it discovers - including an inevitable rash of false positives. It is an entirely different thing to get a well trained and well equipped team of white hat hackers to try and bust into your critical web based systems. Do not get me wrong, Nessus is a spectacular information security tool, but just as people are better than computers at playing the game of go, people are better than automated tools at uncovering system vulnerabilities. This is especially true in the realm of web application vulnerabilities, an area where the available tools have not reached the level of sophistication that Nessus and its commercial counterparts have for general remote host audits.
Jeremiah Gossman has a column on BetaNews that gives an inside look into his web application security outfit, WhiteHat Security. Here is an excerpt.
"With the necessary paperwork signed and account credentials generated, we were ready to go. The URL and username/password were revealed to the racers and the symbolic green flag dropped. The next several seconds we heard nothing but mouse clicks and keyboard tapping.
From past experience we've learned that the fastest way to victory is to target the search boxes first and try for a speedy XSS win. Search boxes are notorious for such insecurities. It's a cheap trick, but it works. Next, it's best to look for input parameters and determine if any of them echo URL query data, indicating another potential spot for XSS.
The first 60 seconds of the race flew by. Nervousness set in because we knew that at any moment someone was going to claim speed-hack victory. Bill Pennington (WhiteHat's VP of Services), in what is becoming a trend, identified the first vulnerability (XSS) in about 1 minute 30 seconds. In classic style, we cried foul because he could arguably only exploit himself with XSS and represented no further risk."
Its one thing to build Nessus on your Linux box, click all tests on, enter a target IP, click go, and watch the test progress bar grow. After hundreds of thousands of Ethernet TX/RX LED flickers, Nessus will present you with a nicely formatted report of any and all vulnerabilities it discovers - including an inevitable rash of false positives. It is an entirely different thing to get a well trained and well equipped team of white hat hackers to try and bust into your critical web based systems. Do not get me wrong, Nessus is a spectacular information security tool, but just as people are better than computers at playing the game of go, people are better than automated tools at uncovering system vulnerabilities. This is especially true in the realm of web application vulnerabilities, an area where the available tools have not reached the level of sophistication that Nessus and its commercial counterparts have for general remote host audits.
Jeremiah Gossman has a column on BetaNews that gives an inside look into his web application security outfit, WhiteHat Security. Here is an excerpt.
"With the necessary paperwork signed and account credentials generated, we were ready to go. The URL and username/password were revealed to the racers and the symbolic green flag dropped. The next several seconds we heard nothing but mouse clicks and keyboard tapping.
From past experience we've learned that the fastest way to victory is to target the search boxes first and try for a speedy XSS win. Search boxes are notorious for such insecurities. It's a cheap trick, but it works. Next, it's best to look for input parameters and determine if any of them echo URL query data, indicating another potential spot for XSS.
The first 60 seconds of the race flew by. Nervousness set in because we knew that at any moment someone was going to claim speed-hack victory. Bill Pennington (WhiteHat's VP of Services), in what is becoming a trend, identified the first vulnerability (XSS) in about 1 minute 30 seconds. In classic style, we cried foul because he could arguably only exploit himself with XSS and represented no further risk."
Subscribe to:
Posts (Atom)
About Me

- thrashor
- Edmonton, Alberta, Canada
- Returned to working as a Management Consultant, specializing in risk, security, and regulatory compliance, with Fujitsu Canada after running the IT shop in the largest library in the South Pacific.

